Private beta
Upload a zip.
Get a launch kit.
GoLiveOS reads your scripts or app, shows what is missing to go live, and generates the deployment files, sign-in, payments and checklist to ship it.
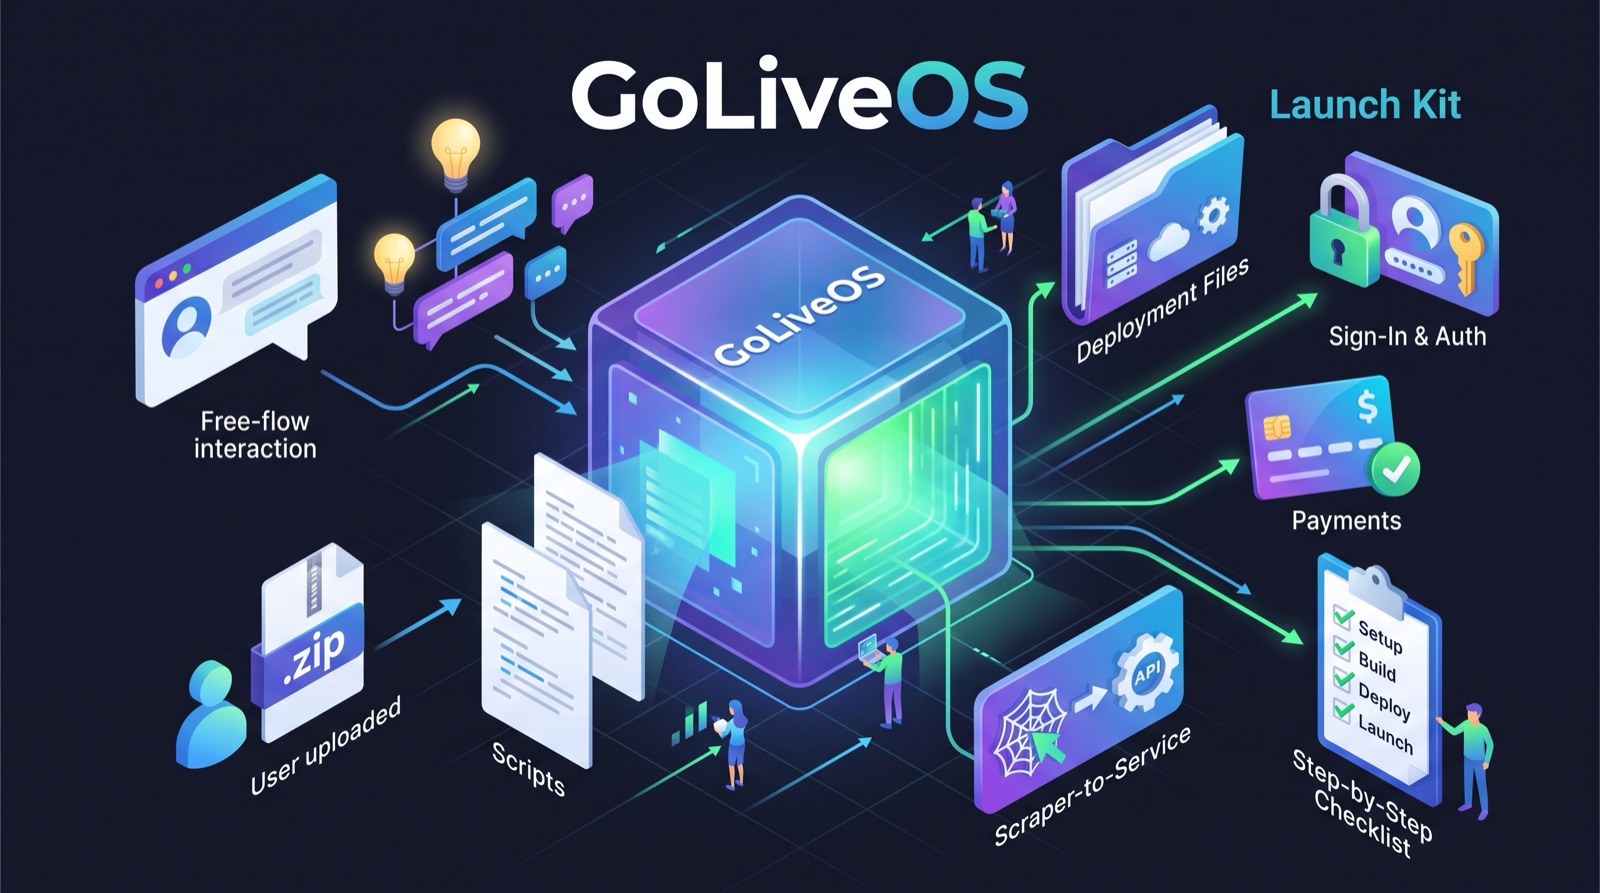
- 19 launch templates
- Node + Python apps and scripts
- Never run your code is read, not executed
- Evidence every check cites your code
From a zip to live in three steps
-
01
Upload
Drop in a
.zip,.tar.gz,.tgzor.tarof your project. A scraper, a script, an API or a full app. GoLiveOS inventories it without installing or running anything.Coming soon: or describe an idea in your own words and turn it into a project.
-
02
Audit
You get a readiness score and a list of checks for hosting, secrets, sign-in and billing. Every finding points at the file and line that proves it.
-
03
Launch
Download a launch kit with the files to deploy, plus a step-by-step checklist you can tick off as you go.
Know what blocks you
The audit is evidence-backed. If it cannot cite a file for a claim, it does not make the claim.
- Hard-coded keys and committed
.envfiles - Missing sign-in or billing on a public endpoint
- Hosting that cannot run your app (browser, disk, long jobs)
- A custom domain checklist for your target host
Example audit Not ready
2 blocking issues
- Blocking: Live Stripe key hard-coded in
server.js - Blocking: Committed
.envexposes a database password - Warning: No sign-in on the Express routes
- Passed: Runs on Node 22 with a container host
Everything in the launch kit
Deployment files
Dockerfile,
fly.tomlorwrangler.toml, pinned and ready for your target.Sign-in and auth
Drop-in JWT verification for Express, Hono, Flask and FastAPI, locked to your audience.
Payments
Stateless Stripe billing with webhook verification, so paid routes stay paid.
Scraper to service
Wrap a script or scraper in an API with a jobs runner, in Node or Python.
Step-by-step checklist
Setup, build, deploy, launch. Check steps off and pick up where you left off.
Free-flow ideas
Coming soon: describe what you want to build and start a project without a zip.
Your code stays inert
- Read-only static analysis, never executed or installed
- The analyzer report records only a salted hash of any secret it finds, never the value
- Each project is private to your account
- Your original archive stays in private storage until you delete the project, and deleting removes it
Read, never run
Uploaded code is treated as hostile. It is unpacked in isolation and parsed for facts, and the audit sees a structured summary, not your source. Your original archive is kept in private storage tied to your account until you delete the project.
Find out what is missing
Upload a zip or paste a public GitHub repository, and get your readiness score in about a minute.
Open the app